ConnectWise suspended Cloud Backup, formerly SkyKick, after identifying unauthorised access to application identities used by the service. It also paused SaaS Security and Cloud Management while remediation and forensic validation continue. Scheduled backups, archive access and restores remain unavailable, while independent researchers have identified suspicious Microsoft 365 sign-ins across customer tenants.[1][3][5]
A shared identity widened the scope
Cloud Backup is a multi-tenant Microsoft 365 application. Todyl says an unauthorised party authenticated to Microsoft Graph as the app itself, using existing consent in monitored tenants.[4]
That access covered mail, attachments, OneDrive, SharePoint, Teams and restore operations. Todyl describes an app-only OAuth flow, so user interaction was unnecessary for the sign-ins examined.[4]
Each organisation must check its app settings, sign-in records and audit coverage.[2][4]
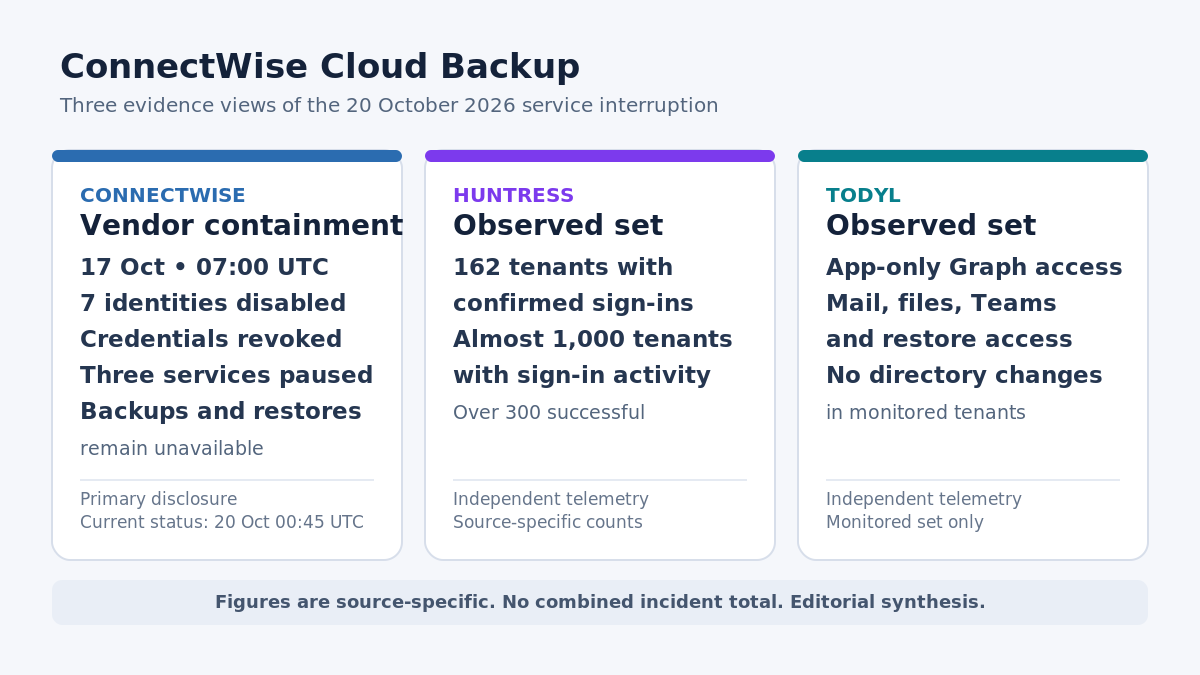
The reported numbers describe different evidence sets
Huntress confirmed unauthorised sign-ins in 162 tenants by 19:00 UTC on 16 October. In a later update it reported almost 1,000 Entra tenants with sign-in activity from the suspicious address and more than 300 successful sign-ins.[3]
These figures describe Huntress’s observed sets. The incident-wide total remains unknown. Cybersecurity Dive reported the same figures and the connected-service suspension.[5]
Todyl found no directory changes, new secrets, consents or role assignments in its monitored tenants. Huntress found no evidence of mailbox or file manipulation in two reviewed tenants, while noting that Microsoft 365 does not log every application read.[3][4]
Containment does not end tenant review
ConnectWise’s 18 October guide tells administrators to keep affected connections disabled, preserve evidence and review service-principal sign-ins, credentials, roles and mailbox activity.[2]
The advisory says stored archives show no indication of compromise, while live-tenant impact remains open. Cloud Backup, SaaS Security and Cloud Management remain suspended, with backups, archive access and restores unavailable.[1]
ConnectWise had not published a restoration time in its 00:45 UTC update on 20 October. It said services would return in controlled phases after remediation and security validation.[1]
The next record matters
Until the next update, the public evidence describes a service interruption with containment in progress and a separate tenant-level investigation. The next useful record will be ConnectWise’s restoration guidance and each tenant’s own audit findings.[1][2]
Sources
[1] Trust Center | Advisories | ConnectWise
[2] Cloud Backup technical investigation and remediation guide
[3] ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks
[4] Investigation: Unauthorized Access Through the ConnectWise Cloud Backup Microsoft 365 App
[5] ConnectWise suspends Cloud Backup service as hacker targets Microsoft 365 users

