The US Cybersecurity and Infrastructure Security Agency has set out a strategy for national cyber defence, critical-infrastructure security and resilience through 2030. Released on 26 October,[1] “Defend, Harden, Prevail” promises to begin a review of core services within 60 days and deliver an approach for implementation and measurement of outcomes within 180 days.[2] Those milestones remain commitments.
The three priorities
Under Defend, CISA proposes coordinating government, industry and international partners, and working with operational-technology owners on asset visibility, anomaly detection and supply-chain integrity.[2][3]
Harden prioritises infrastructure whose disruption would have the greatest consequences. CISA proposes using infrastructure data to direct resources and supporting a National Risk Register. Its criteria include public health, economic continuity and national security.[2]
Prevail covers continuity after disruption: regional advisers, emergency communications and joint planning. The plan refers to 10 regional offices and envisages expanding priority telecommunications using 5G/6G and commercial satellite constellations.[2]
A timetable to test
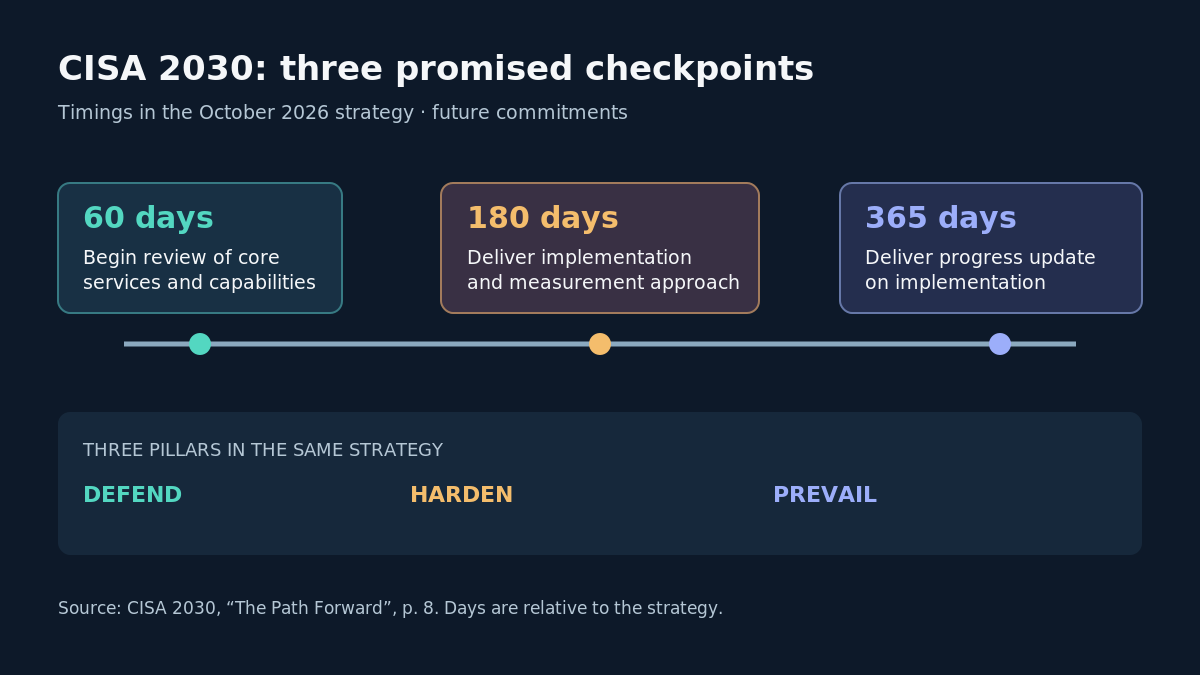
The graphic separates three promised checkpoints. The 60-day review is due to begin within that period. At 180 days CISA promises an implementation and measurement approach; at 365 days, a progress update.[2] Infosecurity Magazine reports the later commitments.[5] Cybersecurity Dive describes the initial review.[4]
Delivery questions
Cybersecurity Dive reports that workforce reductions and changes to industry partnerships could complicate delivery.[4] CISA pledges to build capacity through its regional offices.[2]
A public test will be whether the implementation approach names measures for each pillar and the one-year update reports against them. This is an editorial test of CISA’s timetable.[2]
Sources
[1] CISA release: new national cyber defence strategy (26 October 2026)
[2] CISA 2030 strategic plan (October 2026)

