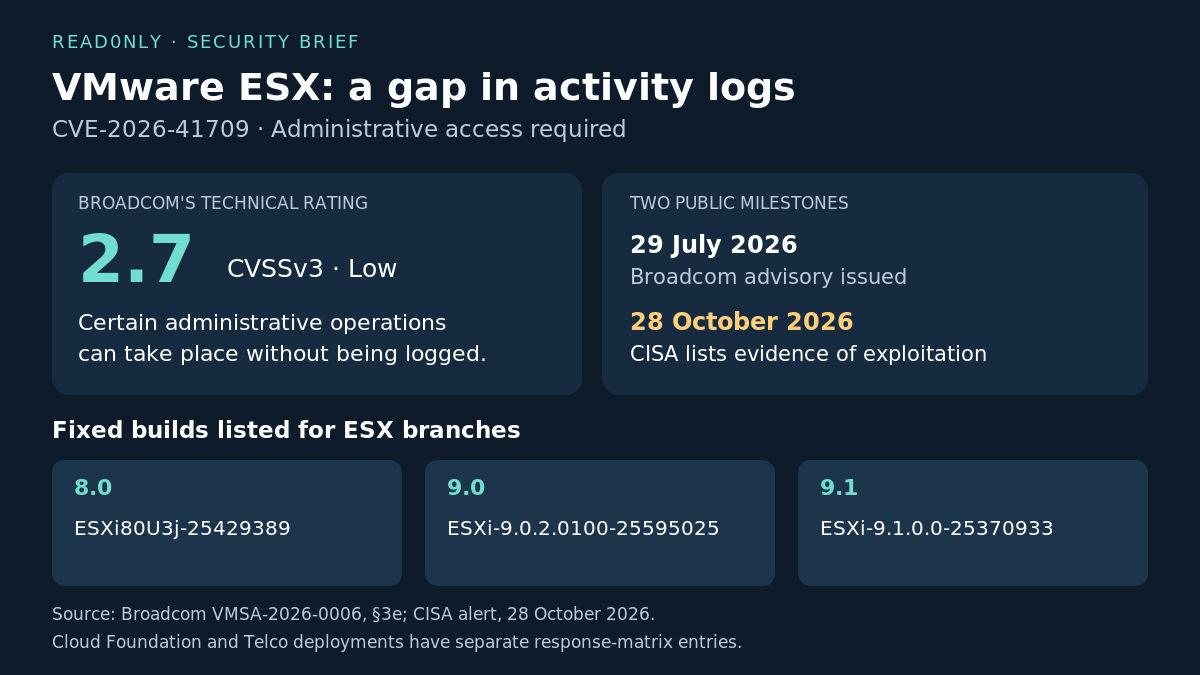
CISA added VMware ESX vulnerability CVE-2026-41709 to its Known Exploited Vulnerabilities catalogue on 28 October, citing evidence of active exploitation.[1] The flaw lets an administrator perform certain operations without those actions being logged.[2] Broadcom rates it Low, with a CVSSv3 base score of 2.7.[2]
What we know Exploitation is recorded by CISA, and Broadcom provides patched versions.[1][2]
What we don't know CISA's 28 October alert gives no victim count, attack timeline or named threat actor.[1]
Why it matters The vulnerability affects the record of administrative activity, making it relevant to investigations after privileged access has been obtained.[2]
Administrative access is the prerequisite
Broadcom's advisory describes an insufficient-logging vulnerability exploitable by a malicious administrator.[2] Its public description says “certain operations” can escape logging, leaving the precise scope of those operations unspecified.[2]
SecurityWeek separately covered the flaw in its reporting on VMware patches, describing the same administrative-access requirement.[4] That report said Broadcom was unaware of exploitation at the time; CISA's October alert supplies the subsequent exploitation finding.[4][1]
The advisory covers several vulnerabilities and carries an overall Critical rating. Its section 3e assigns this specific logging flaw a Low rating of 2.7; the critical VMXNET3 code-execution issue has a separate identifier, CVE-2026-47876.[2]
Taken together, the sources provide two distinct inputs for patch prioritisation: the flaw's technical severity and CISA's evidence that attackers have used it.
Match the patch to the branch
For CVE-2026-41709, Broadcom's response matrix lists ESXi80U3j-25429389 for ESX 8.0, ESXi-9.0.2.0100-25595025 for the 9.0 branch, and ESXi-9.1.0.0-25370933 for the 9.1 branch.[2] Cloud Foundation 5.x has a separate entry pointing to 5.2.4, while Telco Cloud Platform deployments are directed to KB449886.[2]
Broadcom lists no workaround for this vulnerability.[2] CISA's catalogue records 11 November 2026 as the due date, with remediation instructions subject to its risk-based federal guidance; the directive applies to Federal Civilian Executive Branch agencies.[3][1]
For administrators, the useful check is the installed product and build against the matching response-matrix row, including any platform-specific patching instructions.
Sources
[1] CISA: exploited-vulnerability alert, 28 October 2026
[2] Broadcom: VMSA-2026-0006, section 3e


Leave a Reply