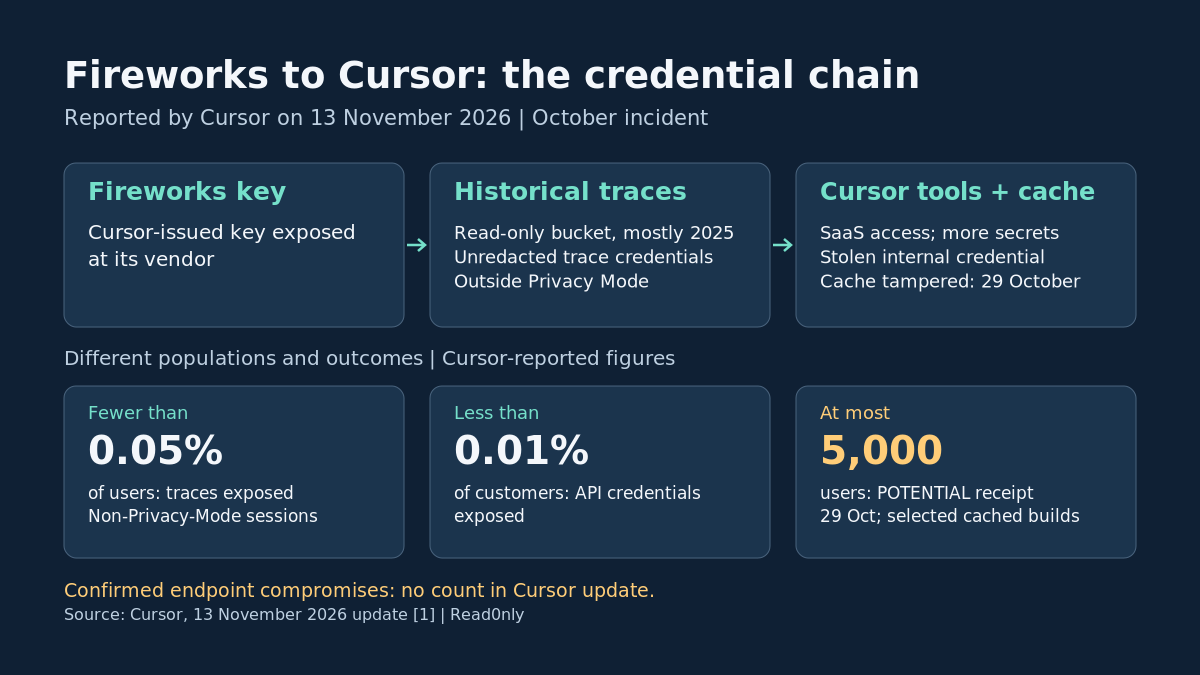
Cursor’s 13 November investigation update traces its October extension incident to an access key exposed at Fireworks AI.[1] The reconstruction adds the credential trail behind the tampered extension covered in our earlier report.[1]
According to Cursor, the key allowed copying from a read-only shared bucket holding coding-agent traces, mostly from 2025 and sessions outside Privacy Mode, retained for model training.[1] Unredacted secrets in some traces opened SaaS tools, archived non-production repositories, support material and further credentials; a stolen internal credential then enabled marketplace-cache tampering on 29 October.[1]
Fireworks’ updated bulletin expands its earlier findings to account and billing data, plus datasets and incomplete models for certain customers.[4] It reports development-machine access on 24 October following a cloud-provider incident; its investigation remains ongoing.[4]
Cursor reports trace exposure for fewer than 0.05% of users and API-credential exposure for fewer than 0.01% of customers.[1] At most 5,000 users potentially received selected cached builds on 29 October 2026.[1] Its update gives no count of confirmed endpoint compromises. SecurityWeek reports Cursor’s account without providing an independent forensic reconstruction.[2]
Cursor says Privacy Mode prompts and code, active inference requests and customer code repositories were unaffected.[1] It has withdrawn Fireworks’ access, moved all inference traffic away from the supplier and cut off access to shared datasets.[1] It believes the incident is contained; the last attacker activity it observed, on 1 November, was blocked.[1]
The company says it emailed administrators specific exposed keys to rotate.[1] For anyone who installed or updated to Anthropic.claude-code 2.1.312 or 2.1.313 from Cursor’s VS Code marketplace on macOS or Windows between 02:27 and 13:35 PT on 29 October 2026, its security notice warns that uninstalling alone may leave persistence behind.[3] It directs affected users to check their systems, remove persistence and rotate credentials accessible from affected hosts from a trusted system.[3]
Sources
- An update on our recent security incident · Cursor
- Cursor Supply Chain Attack Started at Fireworks AI – SecurityWeek
- Security notice — malicious version of Anthropic.claude-code (2.1.312 and 2.1.313) identified in the Cursor VS Code Extension Marketplace · Cursor
- Update on October 2026 security incident | Fireworks AI

